LegalAI[Space]

DSARs on the clock, Article 28 reviews, DPIAs, and a register of what the ICO said this week.

Load the requester's export or the breach timeline into the matter, and work the exemptions or the notification decision against the documents actually there.

Privacy and data protection

Document Review · Hartwell matter · contract screen0/12 filled
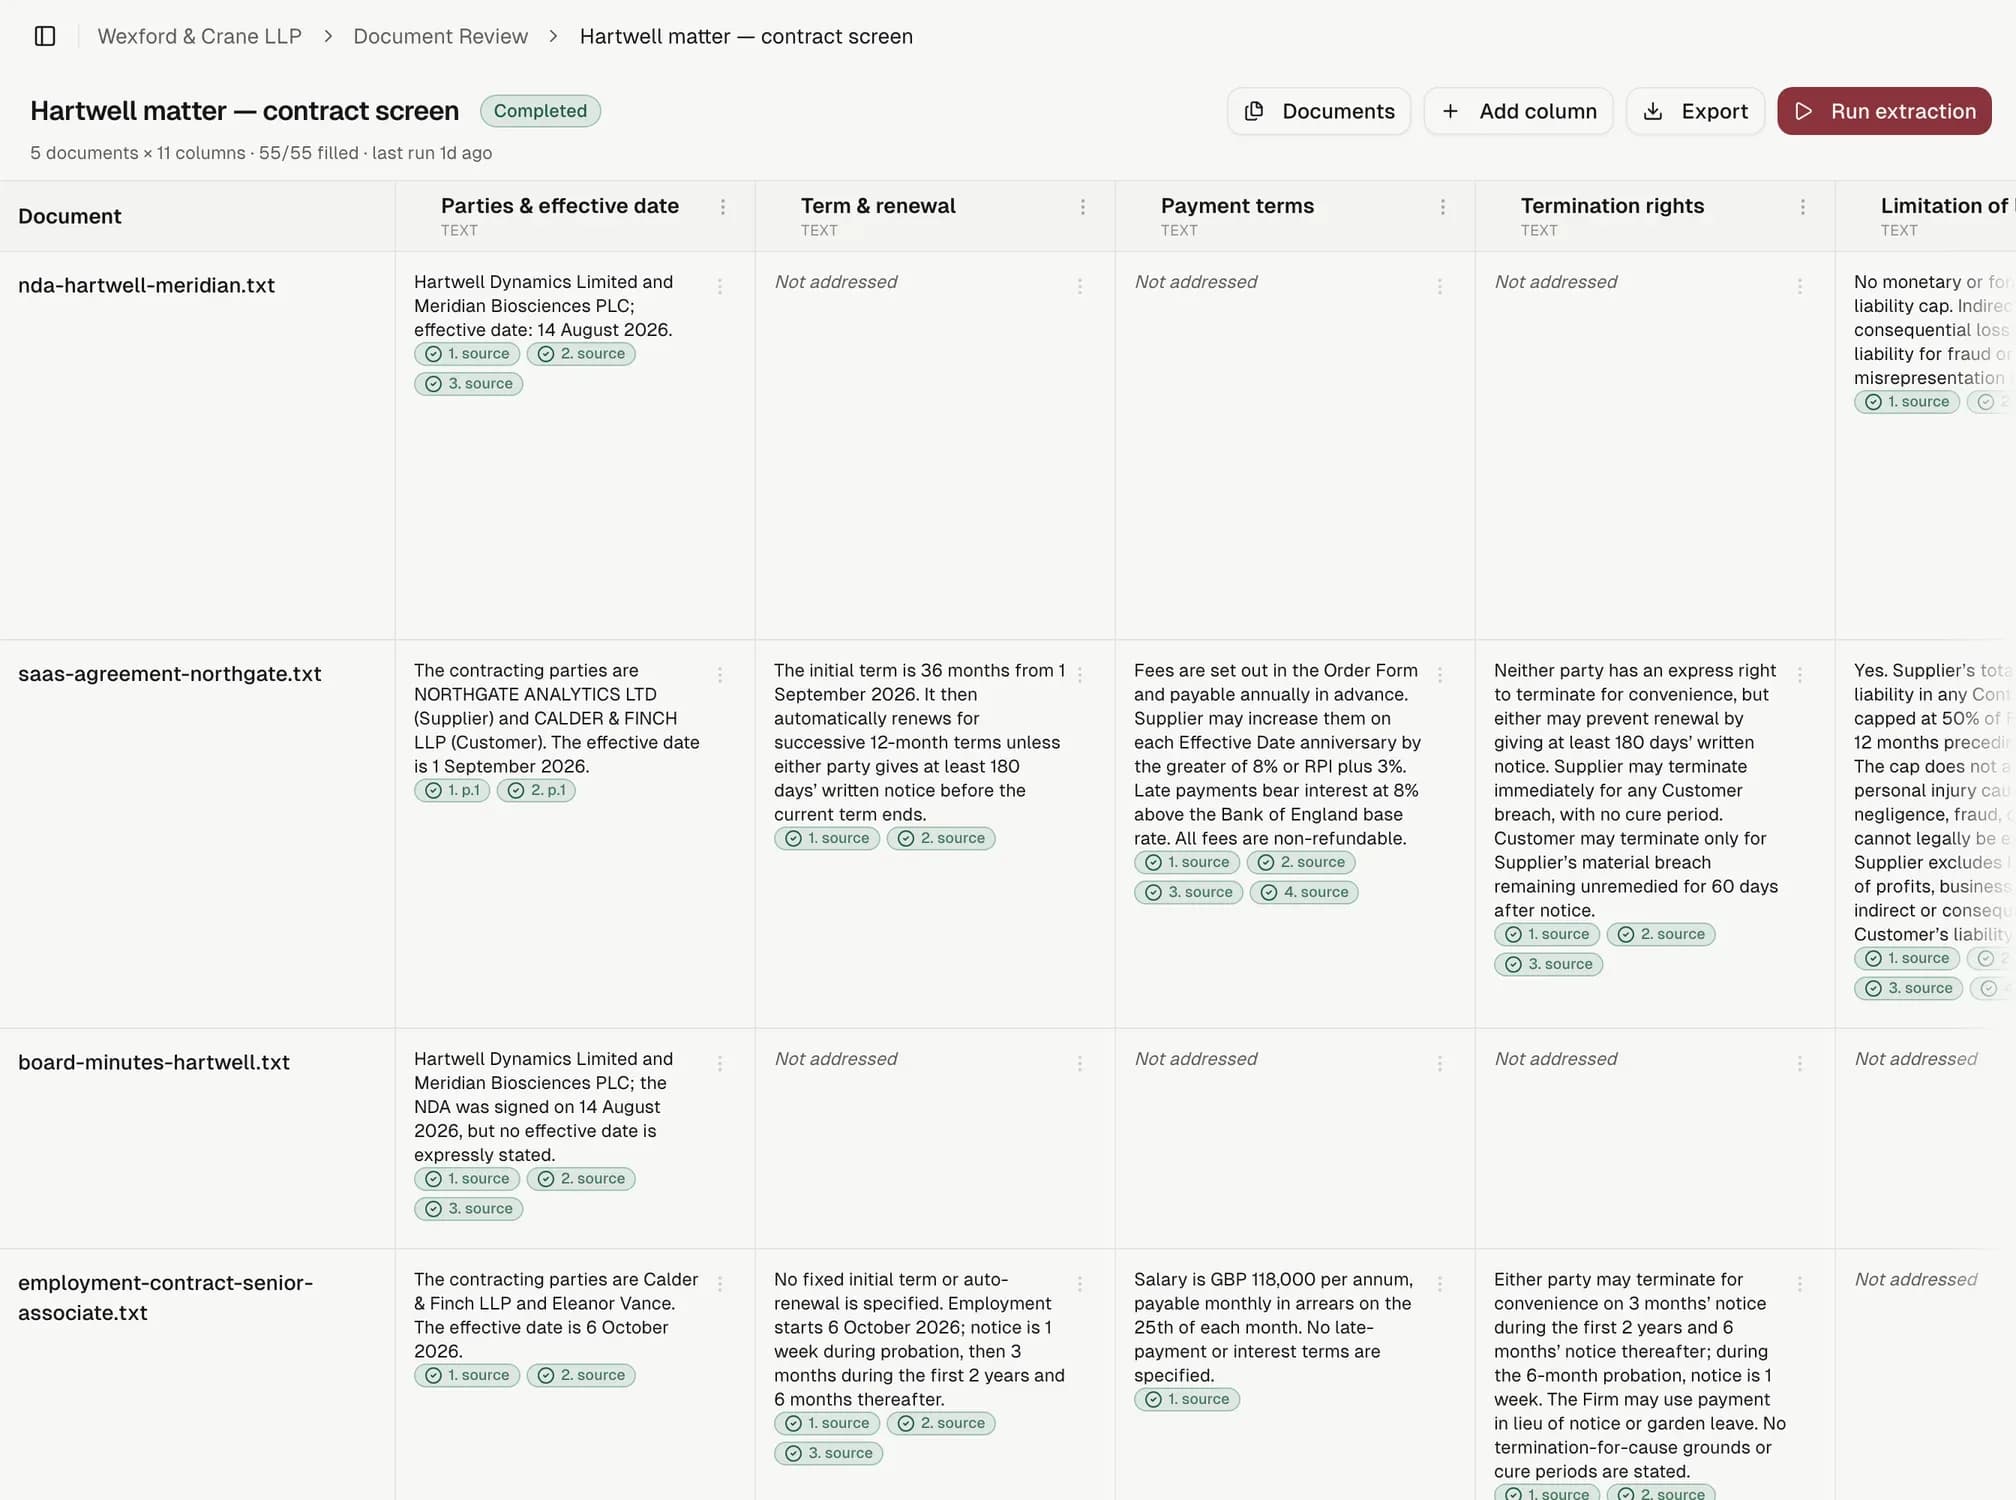
DocumentParties and effective dateTEXTTerm and renewalTEXTLimitation of liabilityTEXTGoverning lawTEXT
nda-hartwell-meridian.txt
saas-agreement-northgate.txt
board-minutes-hartwell.txt
A vendor stack read against the Article 28 questions before a renegotiation letter goes out.

Before

A DSAR arrives on the 3rd and the answer is due on a date the client cannot move, while the exemptions turn on documents nobody has read yet.

A breach like Pendle Group's has a 72-hour notification clock running before anyone has finished working out what actually happened.

Article 28 processor terms are the quiet failure: every client signs dozens, almost nobody reviews them properly, and the gaps only matter after an incident.

After

The Privacy & Data Protection Agent scopes the DSAR, works the exemptions against the documents actually in the matter, and flags the points needing a human decision rather than deciding them.

On a Pendle Group-shaped breach, the agent structures the assessment against the 72-hour clock while the underlying facts are still coming in, so the notification decision is not made against a blank page.

Forty vendor agreements go into a grid against the Article 28 questions you write yourself, the sub-processor and international-transfer columns showing which six need renegotiating.

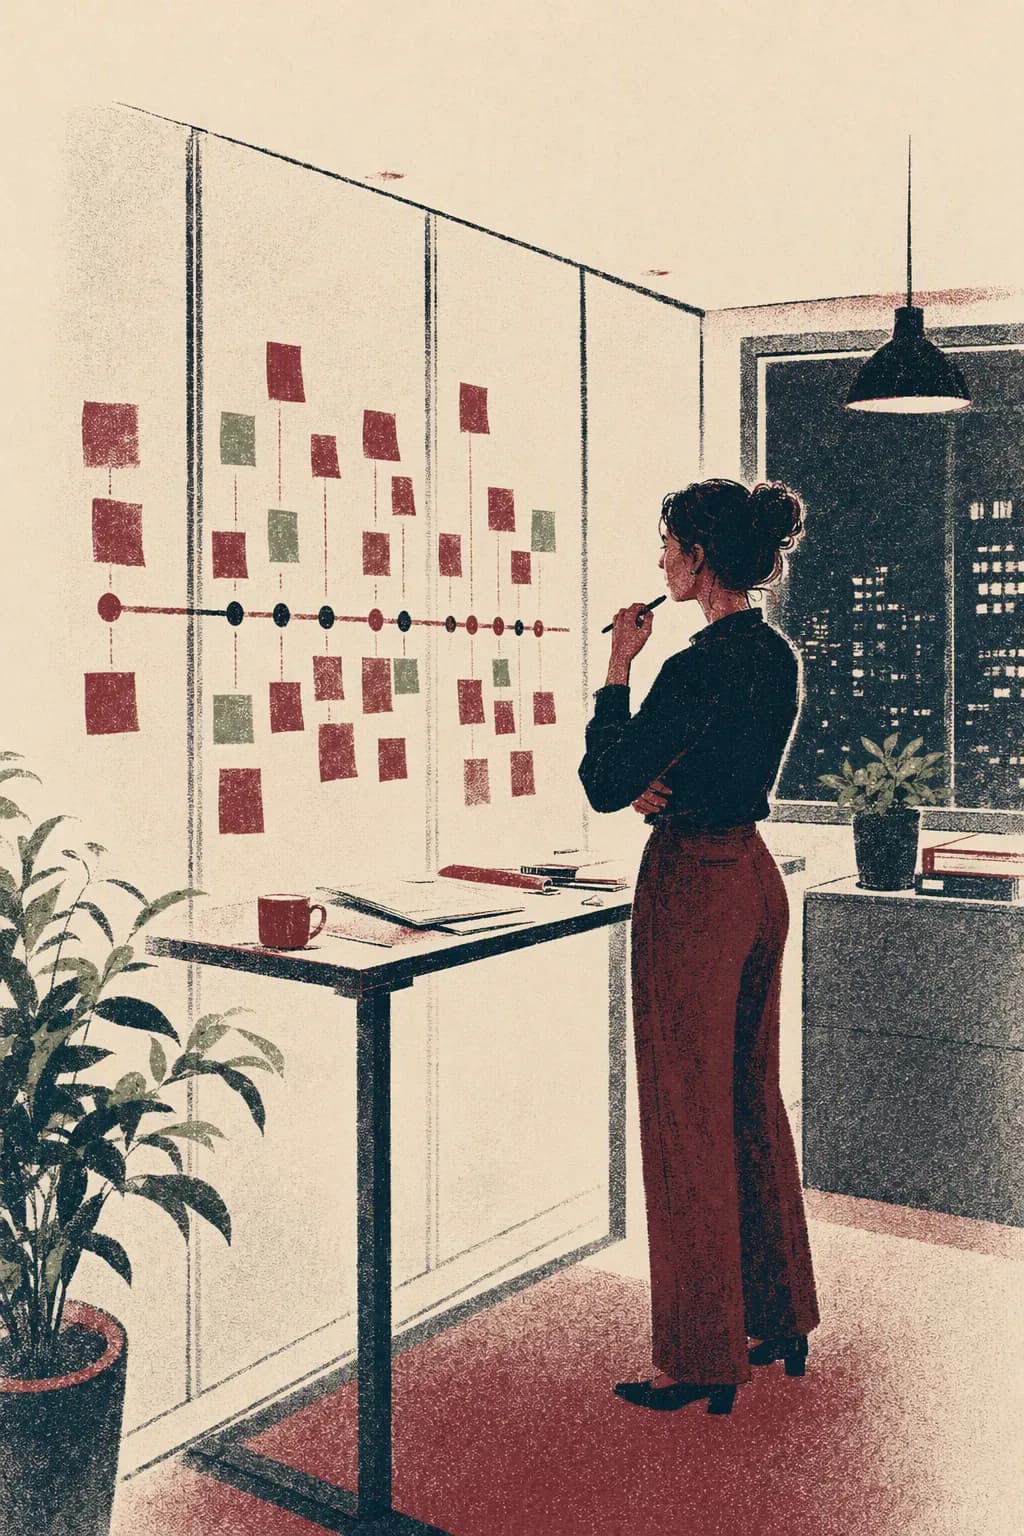
A data protection officer reviewing a breach timeline pinned to a glass wall.

01

Grounded on the matter

The requester's export, the breach timeline or the vendor agreement goes into the matter, and the Privacy & Data Protection Agent reads what is actually there. A PII screen runs on the run itself, with an allow-list so the names you need are kept.

See how matters work
Matters · Project Halcyon · SPA warranties and disclosureOpen

Project Halcyon: SPA warranties and disclosure

Buy-side warranty review, disclosure analysis and cited due-diligence grid.

Client
Halcyon Bidco Ltd
Reference
WC-2026-0412
Practice area
Corporate / M&A
Jurisdiction
England and Wales
Responsible partner
E. Vance
No conflict check on file.

Chat, on this matter

Compare warranties with the disclosure letter.

Three high-priority exceptions require action: the unregistered charge, the change-of-control right and the tribunal claim.

Send a message… (@ to mention tools)BalancedPrepare for
  1. 25 Aug

    Disclosure exceptions matrix

    Chat

  2. 21 Aug

    Disclosure exceptions matrix

    Run · completed · 560 credits

  3. 18 Aug

    Project Halcyon: Disclosure Letter

    Document · indexed

  4. 16 Aug

    Project Halcyon: Share Purchase Agreement

    Document · indexed

  5. 4 Aug

    Matter opened

    Opened

The matter for a breach notification, the statutory deadline set as a key date.

02

A memo, not a chat

The Article 28 grid puts forty vendor agreements down the side and the processing questions across the top: subject matter, sub-processor consent, breach notification timing, deletion at end of term. Each cell carries the quoted contract wording.

See the review grid
Document Review · Hartwell matter · contract screen
A review grid: documents down the side, questions across the top, and a cited answer in every cell.
Forty vendor agreements against the Article 28 questions, six flagged for renegotiation.

03

Verified, then shareable

The ICO's guidance and enforcement notices are fetched directly through the Regulator Retrieval sub-agent, preserving the regulator's own taxonomy, and checked before the memo relies on them. Share the client update as a passcode link with an email gate and an expiry.

See how verification works
Authorities · 14 · Where we looked
#ReferenceVerdict
1

Tillman v Egon Zehnder Ltd

[2019] UKSC 32
not yet checked
2

Working Time Regulations 1998

SI 1998/1833, regs 4 to 5, 10 to 14
not yet checked
3

Coppage v Safety Net Security Ltd

[2013] EWCA Civ 1176
not yet checked
4

UK GDPR, Articles 6 and 9

Retained Regulation (EU) 2016/679
not yet checked
5

Employment Rights Act 1996, s 1

c 18
not yet checked
6

Harlow v Artemis International

[2008] EWHC 1126 (QB)
not yet checked
ICO guidance behind a breach-notification decision, fetched and checked.

What a run costs.

A DSAR response and an Article 28 review are each metered in credits against the matter, so the cost of the statutory clock is visible before it is spent.

See pricing

What you will say before you try it.

The DSAR deadline does not move, and neither does the 72-hour clock.
The Privacy & Data Protection Agent works the exemptions or the notification assessment against the documents in the matter on the timeline you set as a key date, flagging what needs a human decision rather than guessing at one.
See how matters work
Personal data is the whole point of this practice, so where it lives matters.
Files, answers and matter records sit in Microsoft Azure UK with no data leaving the UK region, encrypted in transit and at rest, and are never used to train or fine-tune any model.
Read the security statement
Can we prove the DPIA was done properly?
The audit and compliance register logs the run, the verification result and who signed off, exportable as a spreadsheet or a printable audit bundle for a DPO or a client's security team.
See the audit register
Start free

Run a DSAR workflow on one of your own matters.

No card, ten minutes. Turn on the Data & privacy source pack while you are there.